News

Short summaries of the cyber-crime stories moving in India and globally. We link back to the original source — always.

Brazilian Firm Linked to DDoS Attacks on Local ISPs
Malware

Brazilian Firm Linked to DDoS Attacks on Local ISPs

A Brazilian cybersecurity firm, which specializes in protecting against DDoS (Distributed Denial-of-Service) attacks, has been implicated in enabling a botnet that launched large-scale attacks on other internet service providers in Brazil. The company's CEO claimed that these cyberattacks stemmed from a security breach and suggested that a competitor may be behind the incident, aiming to damage the firm’s reputation. The situation highlights the complexities of cybersecurity, where attackers can exploit vulnerabilities even within protective organizations. Such incidents serve as a reminder of the need for continuous vigilance in network security to safeguard against potential threats. Source: KrebsOnSecurity.

via Krebs on SecurityRead source
Concerns Rise Over New AI Model in Japan's Financial Sector
Malware

Concerns Rise Over New AI Model in Japan's Financial Sector

The recent introduction of a new AI model by Anthropic, referred to as a potential superhacker, has raised concerns among global financial institutions in Japan. While this has sparked panic regarding possible cyber threats, many cybersecurity experts believe that the fears may be overstated. They point out that advanced AI tools can also be used to enhance security measures, suggesting that a balanced view should be adopted. Ongoing dialogues in the cybersecurity community emphasize the importance of not overreacting to technological advancements while remaining vigilant against actual threats. Source: [publication name].

via Dark ReadingRead source
Credential-Stealing Malware Targets SAP-Related npm Packages
Malware

Credential-Stealing Malware Targets SAP-Related npm Packages

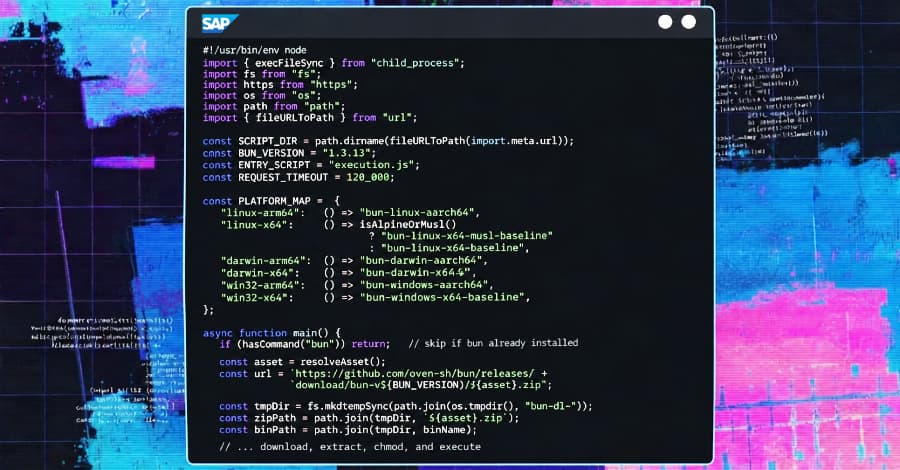
Cybersecurity experts have raised concerns over a new supply chain attack known as mini Shai-Hulud. This campaign has illicitly compromised various npm packages related to SAP's JavaScript and cloud applications, deploying malware designed to steal user credentials. Leading cybersecurity firms, including Aikido Security and Google-owned Wiz, have reported on the ongoing threats posed by this attack. The situation highlights the importance of safeguarding software supply chains and staying vigilant against potential security risks associated with third-party packages. Users and organizations using SAP-related technologies are urged to monitor their systems for any unusual activities and to employ robust cybersecurity measures. Source: CyberSathi.in.

via The Hacker NewsRead source
New Malware Discovered in npm Package Linked to DPRK Attacks
Malware

New Malware Discovered in npm Package Linked to DPRK Attacks

Cybersecurity experts found that a malicious code was embedded within the npm package named '@validate-sdk/v2'. This package is marketed as a software development kit (SDK) for various functions, including hashing and validation. The researchers linked this suspicious activity to North Korean cybercriminals, who are reportedly using artificial intelligence to enhance their attack methods. The package was used as a dependency in a project associated with Anthropic's Claude Opus language model. Users are advised to exercise caution when downloading and utilizing npm packages, as malicious software can pose serious risks. Source: [publication name].

via The Hacker NewsRead source
CERT-In alerts MSMEs to AI-powered cyberattacks
Malware

CERT-In alerts MSMEs to AI-powered cyberattacks

India's Computer Emergency Response Team (CERT-In) has issued a warning to micro, small, and medium enterprises (MSMEs) about escalating cybersecurity threats powered by artificial intelligence. The advisory highlights how attackers are increasingly leveraging AI tools to conduct sophisticated attacks against small businesses, which often lack robust security infrastructure. CERT-In recommends MSMEs implement enhanced security measures, conduct regular employee training on cyber threats, and establish incident response protocols. The warning emphasizes that AI-driven attacks can be more targeted and difficult to detect than traditional methods. Businesses are urged to stay vigilant and report suspicious activities to authorities. Source: The Cyber Express.

via GoogleNews: CERT-In advisoryRead source
Cert-In alerts MSMEs on AI model risks to cybersecurity
Malware

Cert-In alerts MSMEs on AI model risks to cybersecurity

India's Computer Emergency Response Team (Cert-In) has issued a warning to micro, small, and medium enterprises (MSMEs) regarding potential cybercrime threats posed by advanced AI models, including Anthropic's Mythos. The alert highlights how sophisticated artificial intelligence systems could be misused by cybercriminals to conduct large-scale attacks, social engineering schemes, and automated fraud. Cert-In recommends that MSMEs implement robust security protocols, employee training, and monitoring systems to defend against AI-enabled threats. Organizations are advised to stay updated on emerging AI-based attack vectors and adopt preventive measures. Source: The Times of India.

via GoogleNews: CERT-In advisoryRead source
Cert-In warns of AI-driven cyber threats, shares safety measures
Malware

Cert-In warns of AI-driven cyber threats, shares safety measures

India's Computer Emergency Response Team (Cert-In) has issued a warning about emerging cybersecurity threats powered by artificial intelligence. The advisory highlights how AI technologies are being exploited by cybercriminals to launch more sophisticated attacks. Cert-In has outlined specific protection measures for individuals and organizations to defend against these AI-led threats. The guidance emphasizes the importance of staying updated with security patches, using strong authentication methods, and maintaining vigilance against evolving attack vectors. As AI-powered cyberattacks become increasingly prevalent, following these recommended security practices can help reduce vulnerability to malicious activities and data compromise incidents. Source: Business Standard.

via GoogleNews: CERT-In advisoryRead source
CERT-In Warns of Frontier AI Security Risks
Malware

CERT-In Warns of Frontier AI Security Risks

India's Computer Emergency Response Team (CERT-In) has identified frontier artificial intelligence systems as an emerging cybersecurity threat. The warning highlights risks associated with advanced AI technologies that could be exploited for malicious purposes. As AI capabilities expand rapidly, security experts caution that these systems may be leveraged for sophisticated cyber attacks, including automated threat generation and adaptive malware creation. Organizations are advised to implement robust security measures and stay updated on AI-related vulnerabilities. CERT-In continues monitoring the evolving threat landscape to protect India's digital infrastructure from potential AI-driven attacks. Source: The420.in.

via GoogleNews: CERT-In advisoryRead source
Mythos threat prompts Indian agencies to review cyber defenses
Malware

Mythos threat prompts Indian agencies to review cyber defenses

Following the emergence of Mythos, India's cybersecurity authority CERT-In has initiated a comprehensive risk assessment across the telecommunications and banking sectors. Financial institutions and telecom operators are evaluating their current security infrastructure and vulnerability management protocols. The development underscores growing concerns about sophisticated cyber threats targeting critical infrastructure in India. Banks and telecom companies are coordinating with regulatory bodies to strengthen defenses against potential attacks. This proactive measure aims to identify and mitigate weaknesses before adversaries can exploit them, ensuring continued protection of sensitive financial and communications systems across the country. Source: MediaNama.

via GoogleNews: CERT-In advisoryRead source
CERT-In Warns Against AI-Powered Cyber Attacks
Malware

CERT-In Warns Against AI-Powered Cyber Attacks

India's Computer Emergency Response Team (CERT-In) has released a security advisory cautioning MSMEs, organizations, and individuals about the rising threat of artificial intelligence-driven cyber attacks. The advisory highlights how threat actors are increasingly leveraging AI technologies to launch more sophisticated and targeted attacks. CERT-In recommends implementing robust security measures, keeping systems updated, and training employees on cybersecurity best practices to defend against these evolving threats. Organizations are advised to maintain regular backups and establish incident response protocols. The advisory emphasizes the importance of staying vigilant as cybercriminals continue to adopt advanced technologies for malicious purposes. Source: Moneycontrol.com.

via GoogleNews: CERT-In advisoryRead source
Firestarter Malware Evades Cisco Firewall Protections
Malware

Firestarter Malware Evades Cisco Firewall Protections

Security agencies in the U.S. and U.K. have issued warnings regarding a malware called Firestarter. This malicious software has been found to remain active on Cisco Firepower and Secure Firewall devices that utilize Adaptive Security Appliance (ASA) or Firepower Threat Defense (FTD) software. Despite recent security patches and updates intended to counter threats, Firestarter has proven resilient. Users of these Cisco devices are advised to remain vigilant and consider additional security measures to protect their systems from this persistent malware. Regular monitoring and prompt updates are crucial to mitigate potential risks. Source: [publication name].

via BleepingComputerRead source
Cisco Firepower Device Compromised by FIRESTARTER Malware
Malware

Cisco Firepower Device Compromised by FIRESTARTER Malware

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) reported that a Cisco Firepower device used by a federal agency was compromised in September 2025 by malware known as FIRESTARTER. This malware acts as a backdoor, allowing unauthorized remote access to the device. Despite efforts to patch the system, FIRESTARTER reportedly continues to function, posing ongoing security risks. The malware was also assessed by the U.K.'s National Cyber Security Centre (NCSC). This incident highlights vulnerabilities in cybersecurity measures that can be exploited even after updates are applied. Organizations using similar technology should remain vigilant and enhance their security protocols. Source: [publication name].

via The Hacker NewsRead source