News

Short summaries of the cyber-crime stories moving in India and globally. We link back to the original source — always.

Microsoft Issues March 2026 Security Updates for Windows and Software
Malware

Microsoft Issues March 2026 Security Updates for Windows and Software

Microsoft has released its March 2026 security updates, addressing 77 vulnerabilities across its Windows operating systems and additional software applications. Unlike previous months, there are no critical 'zero-day' vulnerabilities reported this time. However, organizations using Windows should prioritize some of these patches due to potential risks. It's important for users and IT administrators to stay informed about the updates to ensure their systems remain secure against possible cyber threats. Regular application of patches can help maintain the safety of user data and enhance overall cybersecurity posture. Source: CyberSathi.in.

via Krebs on SecurityRead source
AI Assistants Influencing Cybersecurity Landscape
Malware

AI Assistants Influencing Cybersecurity Landscape

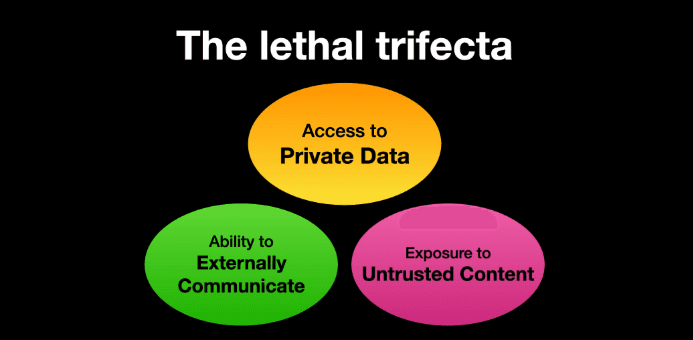
Artificial Intelligence-based assistants are becoming increasingly popular among developers and IT professionals. These autonomous programs can access a user's computer, files, and online services to automate various tasks. However, their rapid adoption is raising new security concerns for organizations. The use of these tools is reshaping security priorities and creating challenges in distinguishing between trusted colleagues and potential insider threats. This blurring of roles is further complicated by the varying levels of expertise among users, from advanced hackers to beginners. As AI becomes more integrated into workplace processes, it is crucial for organizations to address these emerging risks. Source: [publication name].

via Krebs on SecurityRead source
Understanding GetProcessHandleFromHwnd API Security Flaws
Malware

Understanding GetProcessHandleFromHwnd API Security Flaws

A technical analysis reveals significant inaccuracies in Windows documentation for the GetProcessHandleFromHwnd API, which was exploited in a UAC bypass vulnerability via Quick Assist. The API's documented security properties don't match its actual implementation. Claims about UI Access requirements, Windows hook usage, and user-level restrictions were found to be incomplete or incorrect. The API was first introduced in Windows Vista through oleacc.dll. Historical code analysis shows the API has evolved significantly over the years, with the Win32k kernel implementation differing substantially from documented behavior. Understanding these discrepancies is crucial for identifying potential security vulnerabilities in Windows privilege escalation attacks.

via RSS: Google Project ZeroRead source
macOS Audio System Vulnerability Exploited
Malware

macOS Audio System Vulnerability Exploited

A security researcher has detailed the exploitation of CVE-2024-54529, a type confusion vulnerability in Apple's CoreAudio framework affecting the coreaudiod system daemon on macOS. The flaw exists in the com.apple.audio.audiohald Mach service, where message handlers incorrectly assume object types without proper validation. This allows attackers to trigger crashes by manipulating virtual function calls on mistyped objects. The vulnerability was discovered through knowledge-driven fuzzing techniques. The researcher documented the technical process of converting the crash into a working exploit, demonstrating how improper type checking in system-level audio services can be weaponized. Apple users should apply security updates addressing this vulnerability. Source: Security Research Blog.

via RSS: Google Project ZeroRead source
Windows 11 Administrator Protection Feature Had Multiple Vulnerabilities
Malware

Windows 11 Administrator Protection Feature Had Multiple Vulnerabilities

Windows 11's latest version (25H2) introduced Administrator Protection to replace the older User Account Control (UAC) system. This new feature aims to provide stronger security by limiting administrator access only when needed. However, security researchers discovered nine separate vulnerabilities in the feature that could allow attackers to silently gain full administrator privileges. All reported issues were fixed by Microsoft before official release through security update KB5067036 and subsequent bulletins. UAC, introduced in Windows Vista, also faced similar security limitations as it didn't create a hard security boundary. Administrator Protection addresses these weaknesses with improved design. Note: Microsoft disabled the feature on December 1, 2025, due to application compatibility issues. Source: Security research blog.

via RSS: Google Project ZeroRead source
Android Security Gaps: Experts Warn on 0-Click Exploits
Malware

Android Security Gaps: Experts Warn on 0-Click Exploits

Security researchers have identified critical vulnerabilities in Android devices, particularly the Pixel 9, exploitable through 0-click attack chains that require no user interaction. The analysis reveals that audio decoding processes in Google Messages and text-to-speech features create unnecessary attack surfaces by supporting rarely-used codecs like Dolby UDC. These decoders are typically not used for regular messaging but remain active, increasing vulnerability risks. Experts recommend removing uncommonly-used decoders from automatic processing to reduce exposure. The report also warns that AI-powered mobile features, while beneficial, may inadvertently expand 0-click attack surfaces without proper security review. Vendors must carefully evaluate how new features impact device security before deployment to protect users from sophisticated exploitation techniques.

via RSS: Google Project ZeroRead source