News

Short summaries of the cyber-crime stories moving in India and globally. We link back to the original source — always.

TeamPCP Supply Chain Attack Targets Multiple Code Ecosystems
Malware

TeamPCP Supply Chain Attack Targets Multiple Code Ecosystems

Cybersecurity researchers have identified TeamPCP, a threat actor group conducting a widespread supply chain campaign that remained active through May 2024. The group simultaneously operates across three package management ecosystems and has successfully compromised GitHub's internal codebase. Notably, TeamPCP trojanized an official Microsoft-published Python SDK, potentially affecting numerous developers relying on the compromised tool. The attackers have also released their own malicious framework on GitHub, expanding their attack surface. This multi-pronged approach demonstrates sophisticated supply chain attack tactics targeting software developers and organizations worldwide. Indian developers using these ecosystems should remain vigilant and verify package authenticity. Source: Security Research Report.
via RSS: SANS ISC DiaryRead source
Ghost CMS Flaw Exploited to Compromise 700+ Websites
Malware

Ghost CMS Flaw Exploited to Compromise 700+ Websites

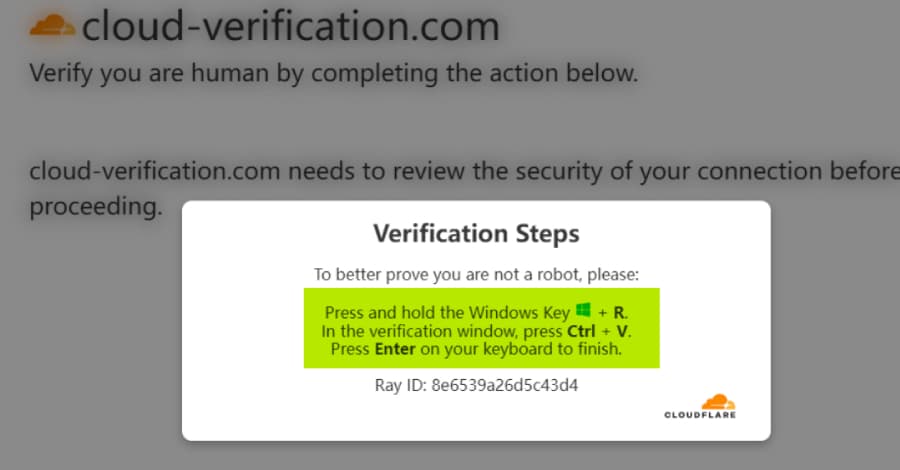
Cybercriminals are actively exploiting CVE-2026-26980, a critical SQL injection vulnerability in Ghost CMS, to compromise over 700 websites. The flaw, rated 9.4 on the CVSS severity scale, exists in Ghost's Content API and allows attackers to inject malicious JavaScript code without authentication. This vulnerability is being weaponized to launch ClickFix attacks, a social engineering technique that deceives users into downloading malware. Security researchers at QiAnXin XLab discovered the widespread exploitation campaign. Website administrators using Ghost CMS are urged to apply security patches immediately to prevent unauthorized data access and malicious code injection on their platforms. Source: Security research report.

via The Hacker NewsRead source
AI-Powered Network Detection Reduces False Security Alerts
Malware

AI-Powered Network Detection Reduces False Security Alerts

Network Detection and Response (NDR) systems have historically faced criticism for generating excessive alerts and noise. However, security teams now deploying NDR with artificial intelligence capabilities report significant improvements in threat detection speed and accuracy. These AI-enhanced systems help security professionals identify threats earlier, prioritize incidents more efficiently, and reduce false positives that waste resources. The evolution of NDR technology addresses longstanding concerns about alert fatigue, enabling teams to focus on genuine security threats rather than filtering through irrelevant notifications. Source: Original cybersecurity publication.

via The Hacker NewsRead source
Lazarus Group Targets Financial Firms with RemotePE Malware
Malware

Lazarus Group Targets Financial Firms with RemotePE Malware

Security researchers have identified RemotePE, a cross-platform malware used by North Korea-linked Lazarus Group to attack financial and cryptocurrency organizations. The malware operates as part of a sophisticated multi-stage attack chain involving two loaders: DPAPILoader and RemotePELoader. DPAPILoader functions to decrypt and execute subsequent malicious payloads, while RemotePELoader facilitates the deployment of RemotePE in memory without writing to disk. This memory-only approach makes detection difficult for traditional security tools. The campaign specifically targets organizations handling digital assets and financial services, highlighting persistent threats to India's growing crypto and fintech sectors. Source: NCC Group/Fox-IT Research.

via RSS: The Hacker NewsRead source
Key Cybersecurity Threats Expected in 2026
Malware

Key Cybersecurity Threats Expected in 2026

Security experts have identified several emerging cybersecurity threats that individuals and organizations should prepare for in 2026. These trends include evolving attack methods targeting both personal and corporate data, increased sophistication in malware development, and new vulnerabilities in digital infrastructure. As cyber threats continue to advance, staying informed about these emerging patterns helps users strengthen their defenses. Indian internet users are particularly advised to maintain updated security practices, enable multi-factor authentication, and remain cautious of suspicious digital activities. Organizations should conduct regular security audits and employee training to combat these anticipated threats effectively. Source: Simplilearn.com.

via GoogleNews: cyber attack IndiaRead source
TrapDoor Malware Found in Popular Code Libraries
Malware

TrapDoor Malware Found in Popular Code Libraries

Security researchers discovered a coordinated attack called TrapDoor targeting three major software package repositories: npm, PyPI, and Crates.io. The campaign distributed malicious code across 34 packages with over 384 versions designed to steal user credentials. Attackers published these packages in waves starting May 22, 2026, exploiting the trust developers place in open-source libraries. This supply chain attack demonstrates how cybercriminals can compromise software development tools to reach thousands of potential victims. Developers using affected packages are at risk of credential theft and system compromise. Source: Security Research Publication.

via RSS: The Hacker NewsRead source
Wireshark 4.6.6 Update Patches Security Flaw
Malware

Wireshark 4.6.6 Update Patches Security Flaw

Wireshark, the widely-used network analysis tool, has released version 4.6.6 with important security updates. The latest release addresses one vulnerability and fixes eleven bugs to improve stability and security. Wireshark is commonly used by IT professionals and cybersecurity experts for monitoring network traffic and diagnosing connectivity issues. Users are advised to update to this version to benefit from the security patch and bug fixes. Keeping network analysis tools updated helps organizations maintain better visibility into their network activities and identify potential threats more effectively. Source: Wireshark.

via RSS: SANS ISC DiaryRead source
LiteSpeed cPanel Plugin Flaw Allows Root Access Attacks
Malware

LiteSpeed cPanel Plugin Flaw Allows Root Access Attacks

A critical vulnerability (CVE-2026-48172) has been discovered in the LiteSpeed cPanel plugin that enables attackers to gain root-level privileges on affected systems. Security researchers report active exploitation of this flaw in the wild. System administrators running LiteSpeed with cPanel should immediately apply available patches to prevent unauthorized access. This vulnerability poses significant risk to web hosting infrastructure and server security across India. Users are urged to update their installations urgently and monitor systems for suspicious activity indicative of compromise. Source: Rescana.

via GoogleNews: vulnerability CVERead source
Security modes in Apple, Google, Meta phones guard against spyware
Malware

Security modes in Apple, Google, Meta phones guard against spyware

Major tech companies have introduced dedicated security modes to protect users from targeted spyware attacks. Apple, Google, and Meta offer enhanced protection features that strengthen device defenses against sophisticated threats. These modes implement stricter security protocols and limit certain functionalities to reduce vulnerability. Users can activate these protective settings through their device preferences. Understanding how these security modes function and when to enable them is crucial for preventing unauthorized surveillance and protecting personal data from malicious actors attempting spyware installation. Source: Security publication.

via RSS: TechCrunch SecurityRead source
AI-Powered Bug Scanning Tools Reveal New Linux Vulnerabilities
Malware

AI-Powered Bug Scanning Tools Reveal New Linux Vulnerabilities

Recent security research has identified three critical vulnerabilities in Linux systems—Dirty Frag, Copy Fail, and Fragesia—discovered through AI-assisted code analysis tools. These findings highlight an emerging trend where artificial intelligence is uncovering previously undetected bugs in widely-used operating systems. The vulnerabilities pose potential security risks for servers and systems relying on Linux infrastructure. Security experts warn that as AI scanning tools become more sophisticated, attackers may also leverage similar technology to identify exploitable flaws. Organizations running Linux systems should monitor security advisories and apply patches promptly to mitigate exposure to these newly-discovered threats. Source: Original publication.

via RSS: The Register SecurityRead source
Understanding Stack Strings in Malware Development
Malware

Understanding Stack Strings in Malware Development

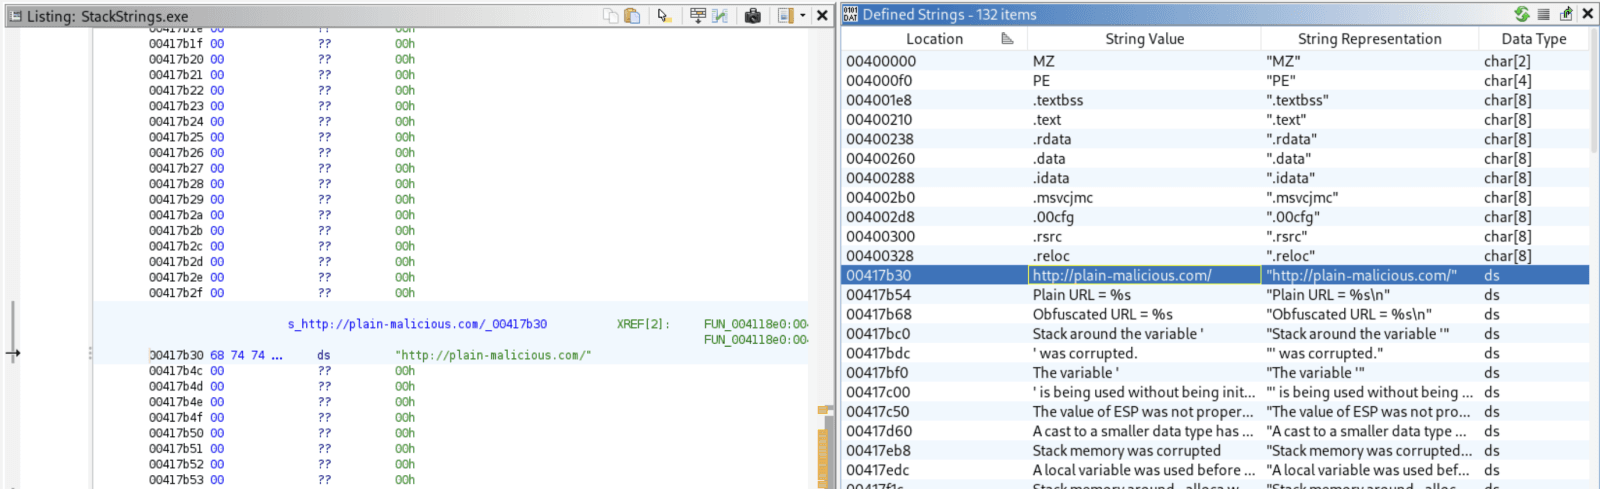
Security training programs like SEC670 focus on red teaming and developing Windows malware, including shellcode and command-control systems. This approach complements traditional malware analysis courses by examining threats from the attacker's perspective rather than through reverse engineering. Understanding malware development techniques, including stack string obfuscation methods used in high-level languages, helps security professionals better recognize and defend against sophisticated cyber threats. Such knowledge enables analysts to identify malicious code patterns and improve detection capabilities. Source: SANS Institute.

via RSS: SANS ISC DiaryRead source
CrackArmor: Critical AppArmor Flaw Exposes Root Access Risk
Malware

CrackArmor: Critical AppArmor Flaw Exposes Root Access Risk

Security researchers have identified a significant vulnerability in AppArmor, a Linux security framework, that could potentially allow attackers to gain root-level access to systems. The flaw, termed CrackArmor, has been detected and documented by Qualys, a prominent cybersecurity firm. This vulnerability affects systems relying on AppArmor for access control and permission management. Organizations using AppArmor-protected Linux environments should prioritize patching and updating their systems to mitigate exploitation risks. System administrators are advised to assess their infrastructure for exposure and apply security updates promptly to prevent unauthorized access escalation.

via GoogleNews: vulnerability CVERead source