News

Short summaries of the cyber-crime stories moving in India and globally. We link back to the original source — always.

F5 BIG-IP Breach Leads to Enterprise Compromise via Confluence
Malware

F5 BIG-IP Breach Leads to Enterprise Compromise via Confluence

Attackers exploited an exposed F5 BIG-IP edge appliance to launch a multi-stage intrusion targeting Linux systems. The threat actors pivoted to an internal Confluence server to steal credentials and compromise user identities. The attack involved attempts at Kerberos relay attacks and lateral movement across the network. Microsoft Defender successfully detected and blocked the attack chain, providing insights into how such edge appliance compromises can escalate into enterprise-wide threats. Organizations should secure exposed edge devices and monitor for suspicious lateral movement activities. Source: Microsoft Security Blog.

via RSS: Microsoft SecurityRead source
Clothing Brand Website Compromised in Malware Distribution Attack
Malware

Clothing Brand Website Compromised in Malware Distribution Attack

A clothing brand's website was hijacked by cybercriminals who attempted to distribute malware to visitors. Users on social media platforms reported the compromise, which led to the website being taken offline. The attackers had modified the site to trick unsuspecting users into downloading malicious software. Website hijacking incidents like these highlight the importance of maintaining strong security measures and regularly monitoring for unauthorized access. Users should avoid clicking suspicious links or downloading files from compromised websites and keep their systems updated with latest security patches. Source: Security Reports.

via RSS: TechCrunch SecurityRead source
Drupal SQL Injection Flaw Added to Active Threat List
Malware

Drupal SQL Injection Flaw Added to Active Threat List

India's cybersecurity teams should note that CISA, the US Cybersecurity and Infrastructure Security Agency, has added CVE-2026-9082, a critical SQL injection vulnerability in Drupal Core, to its Known Exploited Vulnerabilities catalog. This designation indicates active exploitation by threat actors. While CISA's mandate applies to US federal agencies, the agency recommends all organizations globally prioritize patching this vulnerability as part of standard security practices. SQL injection flaws remain favored attack vectors for cybercriminals targeting enterprise systems. Organizations running Drupal should apply available patches immediately to prevent potential compromise. Source: CISA.

via RSS: CISA AlertsRead source
Chinese Hackers Target EU Governments Using Discord, Microsoft Tools
Malware

Chinese Hackers Target EU Governments Using Discord, Microsoft Tools

An advanced persistent threat group linked to China has conducted cyberattacks against European government agencies using legitimate platforms like Discord and Microsoft Graph APIs as command-and-control channels. The attackers employed SOCKS proxies including SoftEther VPN to mask their activities and establish secure tunneling between compromised systems and attacker infrastructure. This sophisticated approach allowed the group to evade detection by blending malicious traffic with normal communications. Security researchers identified this campaign as part of a broader espionage operation targeting sensitive government networks across the EU region. Source: Cybersecurity publication.

via RSS: Dark ReadingRead source
Ottawa Man Arrested for Operating Kimwolf IoT Botnet
Malware

Ottawa Man Arrested for Operating Kimwolf IoT Botnet

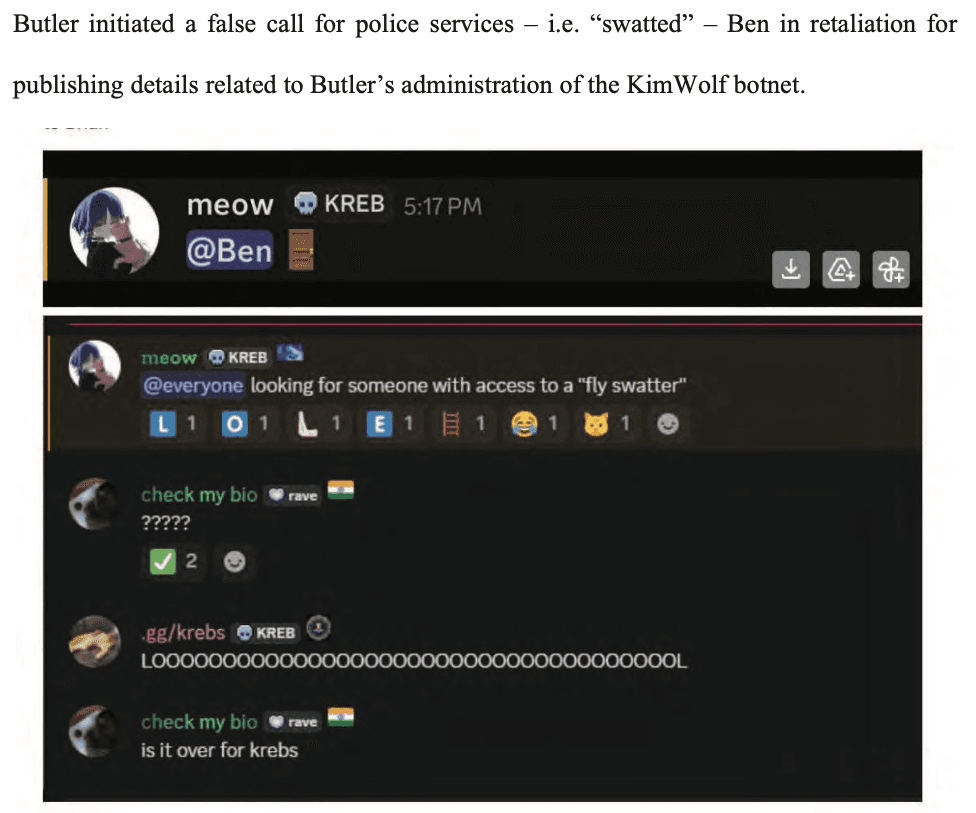
A 23-year-old from Ottawa has been arrested by Canadian authorities for allegedly developing and running Kimwolf, a rapidly spreading botnet targeting Internet-of-Things devices. The malicious software compromised millions of devices to launch large-scale DDoS attacks over six months. The suspect faces criminal hacking charges in both Canada and the United States after launching DDoS, doxing, and swatting attacks against security researchers and journalists. The arrest follows public identification of the accused in early 2026 following these coordinated cyber attacks. Source: KrebsOnSecurity.

via Krebs on SecurityRead source
AI Model Used to Discover macOS Kernel Vulnerability
Malware

AI Model Used to Discover macOS Kernel Vulnerability

Researchers utilized Anthropic's Mythos AI model to identify and exploit a kernel memory corruption vulnerability in Apple's M5 processor. The discovery highlights emerging risks where advanced AI systems can be leveraged to uncover critical security flaws in operating systems. Kernel-level vulnerabilities are particularly dangerous as they can grant attackers complete system control and bypass security protections. Apple users running M5-based devices should monitor for security patches addressing this issue. This incident underscores the dual-use nature of AI technologies and the importance of responsible disclosure practices in cybersecurity research. Source: News Article.

via RSS: Schneier on SecurityRead source
Microsoft Releases May 2026 Security Updates
Malware

Microsoft Releases May 2026 Security Updates

Microsoft has announced new security updates designed to enhance visibility, control, and protection across interconnected systems. The updates focus on addressing emerging threats as organizations increasingly adopt artificial intelligence. These enhancements aim to provide comprehensive security coverage for expanding digital ecosystems. The improvements are part of Microsoft's ongoing commitment to securing enterprise environments against evolving cyber threats. Organizations are encouraged to review the latest security features and implement them to strengthen their defensive posture. Source: Microsoft Security Blog.

via RSS: Microsoft SecurityRead source
Microsoft Alerts Users to New Defender Security Flaws
Malware

Microsoft Alerts Users to New Defender Security Flaws

Microsoft has issued a warning about previously unknown vulnerabilities in its Windows Defender security software that are being actively exploited by attackers. These zero-day flaws allow threat actors to bypass security protections and potentially compromise affected systems. The vulnerabilities represent a significant risk to users who rely on Defender as their primary antivirus solution. Microsoft is urging users to apply security updates and implement additional protective measures. The company is actively investigating the scope of attacks and working on patches to address these critical security gaps. Users should remain vigilant and monitor their systems for suspicious activity. Source: Microsoft Security Advisory.

via HN: zero dayRead source
Website Brand Hijacking Attack Exploits Content Delivery Systems
Malware

Website Brand Hijacking Attack Exploits Content Delivery Systems

Security researchers have identified an attack technique called Underminr that exploits domain-fronting vulnerabilities in content delivery networks. This method allows attackers to intercept and modify web requests while masking their malicious activity behind trusted websites. By leveraging legitimate domains, threat actors can hijack a website's brand and redirect users without detection. This attack poses significant risks to businesses and users who may unknowingly interact with compromised content. Organizations using content delivery services should review their security configurations and implement additional safeguards to prevent unauthorized request manipulation and brand misuse. Source: Cybersecurity Publication.

via RSS: Dark ReadingRead source
CISA Adds Two Active Exploited Vulnerabilities to Alert List
Malware

CISA Adds Two Active Exploited Vulnerabilities to Alert List

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has identified two vulnerabilities actively being exploited by attackers: CVE-2025-34291 in Langflow (origin validation flaw) and CVE-2026-34926 in Trend Micro Apex One (directory traversal issue). These flaws are now part of CISA's Known Exploited Vulnerabilities Catalog, a continuously updated list of security risks threatening critical systems. While U.S. federal agencies must patch these vulnerabilities immediately under directive BOD 22-01, CISA recommends all organizations—including Indian enterprises—prioritize fixing these issues to prevent cyberattacks. Organizations should integrate KEV Catalog monitoring into their vulnerability management strategies. Source: CISA.

via RSS: CISA AlertsRead source
AI Essential for Defending Against Cyber Attacks in India
Malware

AI Essential for Defending Against Cyber Attacks in India

As cyber threats intensify across India, artificial intelligence has become crucial for effective defense mechanisms. Organizations and individuals must adopt AI-powered security solutions to combat evolving attack vectors. Traditional security measures alone are insufficient against sophisticated cyber threats that target Indian businesses and citizens. AI enables real-time threat detection, automated response systems, and predictive analytics to identify vulnerabilities before exploitation. Experts emphasize that without AI integration in cybersecurity infrastructure, Indian organizations face significant risks of data breaches, financial loss, and operational disruption. Implementing AI-driven security frameworks is now considered essential rather than optional for protecting critical digital assets. Source: Whalesbook.

via GoogleNews: cyber attack IndiaRead source
Malicious npm Packages Steal CI/CD Credentials from Developers
Malware

Malicious npm Packages Steal CI/CD Credentials from Developers

Hackers compromised @antv npm packages to distribute malware called Mini Shai-Hulud, targeting developers' automation systems. The malicious code activates during package installation and extracts sensitive credentials from popular platforms including GitHub, AWS, Kubernetes, Vault, npm registry, and 1Password. This attack specifically impacts Linux-based development environments and poses significant risk to organizations relying on automated software deployment pipelines. Developers should immediately review their npm dependencies and update to verified versions. Source: Microsoft Security Blog.

via RSS: Microsoft SecurityRead source