SIM-swap fraud: when your phone stops working in the middle of the day
SIM-swap fraud in India: how attackers steal your number, divert OTPs, and drain UPI/bank accounts — warning signs, the 45-minute response, and how to lock your SIM.
What SIM-swap actually is
Your mobile number is not just for calls. In India it is the key to SMS OTPs for UPI, net banking, email recovery, WhatsApp, and dozens of logins. In a SIM-swap (also called SIM hijack / SIM port-out fraud), an attacker convinces your telecom operator that they are you and that they need a replacement SIM for your number.
Once the telco activates the new SIM in the attacker’s handset:
- Your phone loses signal — often suddenly, mid-day.
- Their phone starts receiving your SMS OTPs and calls.
- They reset passwords or approve transfers using those OTPs.
- Money leaves via UPI, cards, or linked wallets — often within minutes.
This is not “hacking your phone.” It is taking control of your number at the network level.
Why the SIM matters (and what a slot looks like)
Every connection that needs your number ultimately depends on a SIM / eSIM profile registered with Airtel, Jio, Vi, BSNL, or another operator. Physical SIMs sit in a tray or in devices like portable hotspots; eSIMs are digital but can still be re-issued through operator processes.
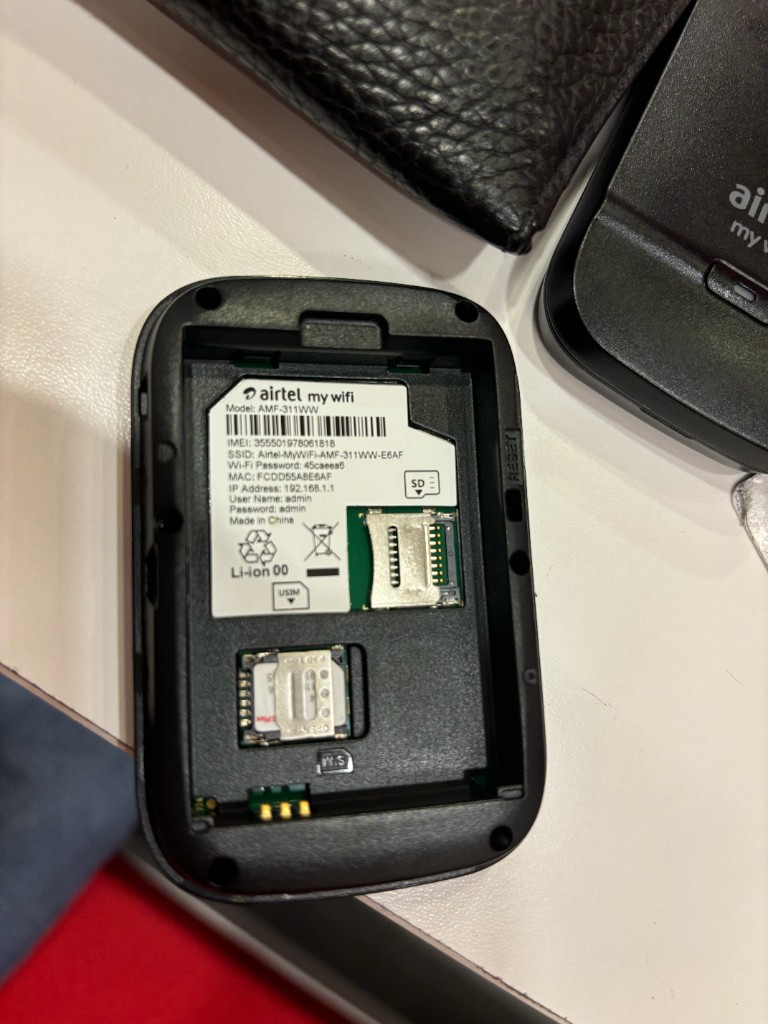
Attackers do not need your phone. They need the operator to point your MSISDN (mobile number) at a SIM they hold.
How the attack usually unfolds in India
1. Reconnaissance
Scammers gather enough identity clues to pass a careless KYC check or social-engineer a store / call-centre agent: full name, address, DOB, last recharge pattern, Aadhaar-linked hints from leaks, photos of ID from phishing, or details from a previous data breach.
2. Social engineering the telco
Common stories: “SIM lost/damaged,” “phone stolen,” “need duplicate SIM urgently,” sometimes with forged or partial documents. In weaker processes, a visit to a franchise store or a scripted call is enough. MNP / port-out abuse is a related variant — the number is moved to another operator under false authority.
3. Your line goes dead
You see No Service / Emergency calls only while colleagues still have full bars. You may get a late SMS about a SIM change you did not request — or none at all.
4. OTP harvest and drain
With SMS in their control they:
- Trigger “forgot password” on email and bank apps
- Approve UPI / card OTPs
- Take over WhatsApp (OTP on SMS) and message contacts for more money
Related reading: How UPI fraud works · WhatsApp scams in India · The UPI Trap
Warning signs — treat these as an emergency
- Sudden no service when others around you have coverage
- Telco SMS about SIM change / duplicate SIM / MNP you did not start
- Calls asking you to read an OTP aloud “for verification”
- WhatsApp logged out + “code was sent to your phone” while your phone has no SMS
- Bank / UPI alerts for transactions you did not do — especially right after signal loss
The 45-minute window (do this in order)
Speed matters more than perfect wording. Borrow any working phone.
-
Call your bank / card issuer 24×7 fraud desk first — not the telco.
Freeze debit/credit cards, block UPI on the account, ask them to flag the mobile number as compromised. Money moves on OTPs; freeze stops the bleeding. -
Call your telecom operator next.
Report unauthorised SIM swap / duplicate SIM. Demand immediate reverse / deactivation of the attacker’s SIM and restoration of your line. Ask for a SIM-change lock / port-out PIN / customer password so the same trick is harder next time. Note the complaint / SR number. -
File on cybercrime.gov.in and call 1930 the same day.
A timestamped complaint is your strongest lever for bank follow-up and investigation. See: What happens if you call 1930? · How to report a cyber crime in India -
Rotate credentials that depended on SMS 2FA.
Email (do this early — it resets everything else), banking apps, UPI PINs after the bank guides you, DigiLocker, income-tax / government logins, social accounts. Prefer authenticator-app 2FA going forward. -
Preserve evidence.
Screenshots of no-service, telco SMS, bank SMS/UTR, WhatsApp logout mails, SR numbers. You will need them for the bank dispute and police/cyber cell.
If you are past the first hour, still do all of the above — odds fall with time, but an official trail still matters: UPI report after 7 days.
Preventing the next SIM-swap
- Move 2FA off SMS wherever the app allows — Authy, Google Authenticator, Microsoft Authenticator, or a password manager TOTP. SMS OTP is convenient for attackers who own your SIM.
- Ask your operator for port-out / SIM issuance protection (extra PIN, LRN lock, do-not-port, video KYC-only reissue — names vary by telco).
- Never read an OTP on a call or share it on WhatsApp. Banks and telcos that are legitimate will not ask you to dictate a live OTP to a stranger.
- After any phone theft or loss, report to the telco before you sleep — do not wait for “maybe it turns up.”
- Treat data breaches that include your phone + DOB + address as SIM-swap fuel: What a data-breach notification means.
- For voice “family emergency” scams that arrive while your line is weird, use callback rules: Deepfake voice fraud.
Frequently asked questions
Is SIM-swap the same as someone cloning my phone?
No. Cloning old magnetic cards is a different era. Modern SIM-swap is operator-side reassignment of your number to a SIM the criminal controls (or fraudulent MNP).
Can this happen with eSIM?
Yes. If the operator issues a new eSIM profile to an attacker’s device, the effect is the same: your profile dies, theirs receives OTPs.
Why call the bank before the telco?
Because OTPs may already be flowing to the attacker. Freezing cards/UPI limits damage while the telco works on reversing the SIM — both are urgent; bank freeze is usually faster against money loss.
Will I get my money back?
Sometimes partially, if you freeze and report within hours and the funds are still in reachable mule accounts. There is no guarantee. Documentation and speed decide most of the outcome.
Does Jio / Airtel / Vi “official app” KYC make me safe?
Stronger processes help, but social engineering and insider/franchise abuse still occur. Defence in depth = SIM locks + non-SMS 2FA + fast freeze habits.
Official resources
- National Cyber Crime Reporting Portal · Helpline 1930
- CERT-In
- Sanchar Saathi / DoT citizen tools (where available for your operator workflow)
- Reserve Bank of India
Related reading on CyberSathi
Read next
Social Engineering
WhatsApp Bank Scam: Is Replying "NO" Dangerous? Safety Tips for India
Social Engineering
Why Growing Trust in Digital Payments Leaves Indians More Exposed to Cybercrime: The Convenience Paradox Explained
Social Engineering